Chaining the Unchainable: Finding and Exploiting Logic Flaws in Modern Web Architectures
Most scanners will never find these bugs. This talk is about what happens when you chain enough of them together anyway. Spoiler: it ends in RCE and full tenant isolation bypass. Business logic flaws are unglamorous. They don't have CVEs, they don't get blog posts, and individually they'll barely register as medium severity on most reports. But in the microservice-heavy, federated identity, multi-tenant environments most organisations are running today, these small mismatches compound. The interesting stuff happens at the joins, like where an API gateway hands off to a downstream service, where an event queue trusts state it shouldn't, or where OAuth flows have one assumption too many baked in. This session walks through three attack chains pulled from real engagements. This is not sanitised theory. We will look at actual proxy logs, HTTP pairs, and the exact moment each system broke. The three paths covered include: 1. Race conditions in async queues: Abusing state validation gaps in event-driven architectures to push through unauthorised transactions. 2. Token propagation abuse: Exploiting the trust gap between an API gateway and its downstream services to chain into deep IDOR. 3. OAuth state-machine quirks: Turning minor implementation oversights into persistent session hijacking. The goal isn't just to show what broke. Attendees will come away with a method for reading an architecture diagram and spotting where the logic synchronisation is weakest, a framework for building these chains deliberately, and concrete design-layer fixes that actually address the root cause rather than just patching symptoms. Key Takeaways for Attendees: - A clear method for analyzing an architecture diagram to spot where logic synchronization is most vulnerable. - An adversarial framework for systematically building exploit chains out of low-severity context flaws. - Concrete, design-layer remediation strategies that address the root cause of these architectural gaps.
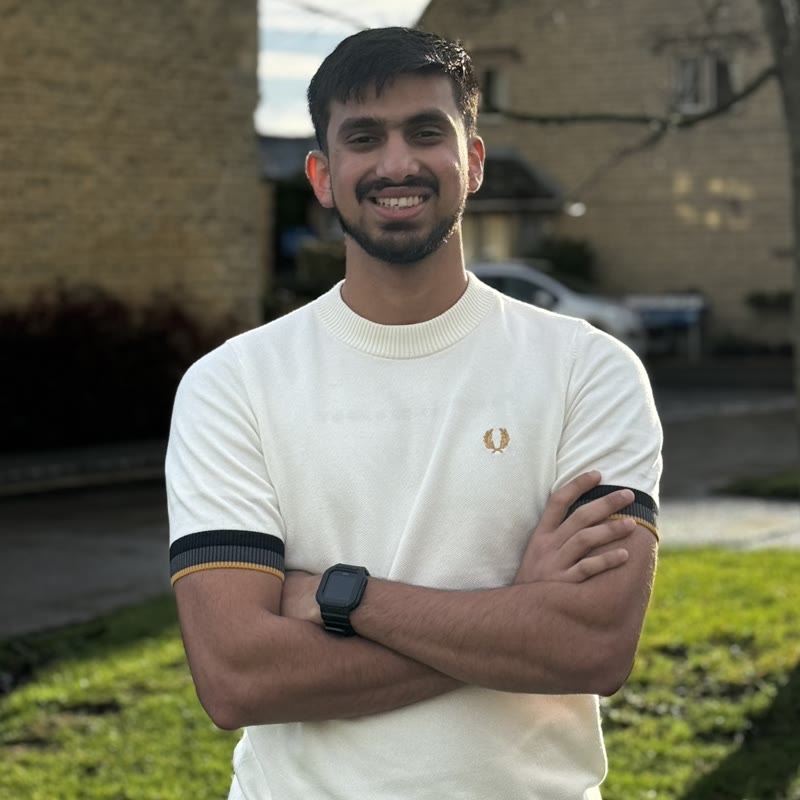
Raj Dhruv
Application Security Specialist at Black Duck I'm an Application Security Specialist at Black Duck, spending my days handling penetration testing, vulnerability assessments, and digging into the weeds of web app flaws. Before this, I was a Machine Learning Researcher at Rapid7, where I built models to predict and filter out false-positive noise inside InsightIDR. I also dropped by Ulster University recently as a guest lecturer to talk to the students about real-world security engineering, and I hold an MSc in Applied Cyber Security from Queen's University Belfast. I like breaking things, figuring out why complex logic fails, and making sure developers have the actual blueprints to fix it.